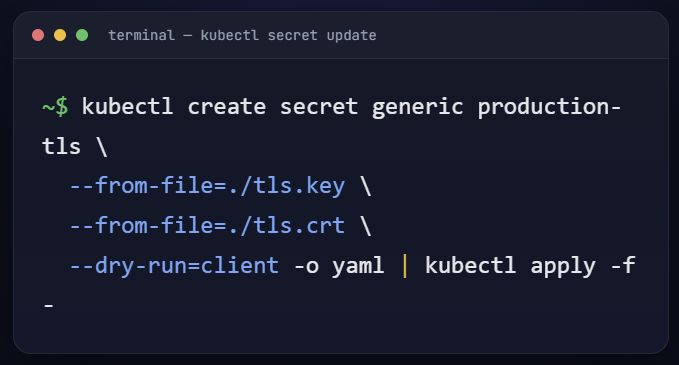
A small Kubernetes tip that saves time when updating TLS secrets. If your secret is generated from files, you do not need to delete and recreate it manually:
kubectl create secret generic production-tls \
  --from-file=./tls.key \
  --from-file=./tls.crt \
  --dry-run=client -o yaml | kubectl apply -f -
This is a clean way to update a secret in a repeatable way, especially in scripts or CI/CD pipelines.